58 lines1.62 KB
Containerised time service with Chrony
MILOUD NECILI
Fraîche Flow · IT Systems Integration
Project objective
Provide a containerised time service and distinguish running status, port exposure and what monitoring proves.
My implementation
- Ran the
chronycontainer using thecturra/ntpimage. - Published UDP port 123 on the host.
- Checked the Docker health status.
- Added Chrony to the central Kuma overview.
Technical context
| Container | chrony |
|---|---|
| Image | cturra/ntp:latest |
| Port | 123/UDP |
| Kuma check | Ping to the container name; no NTP protocol test |
Result
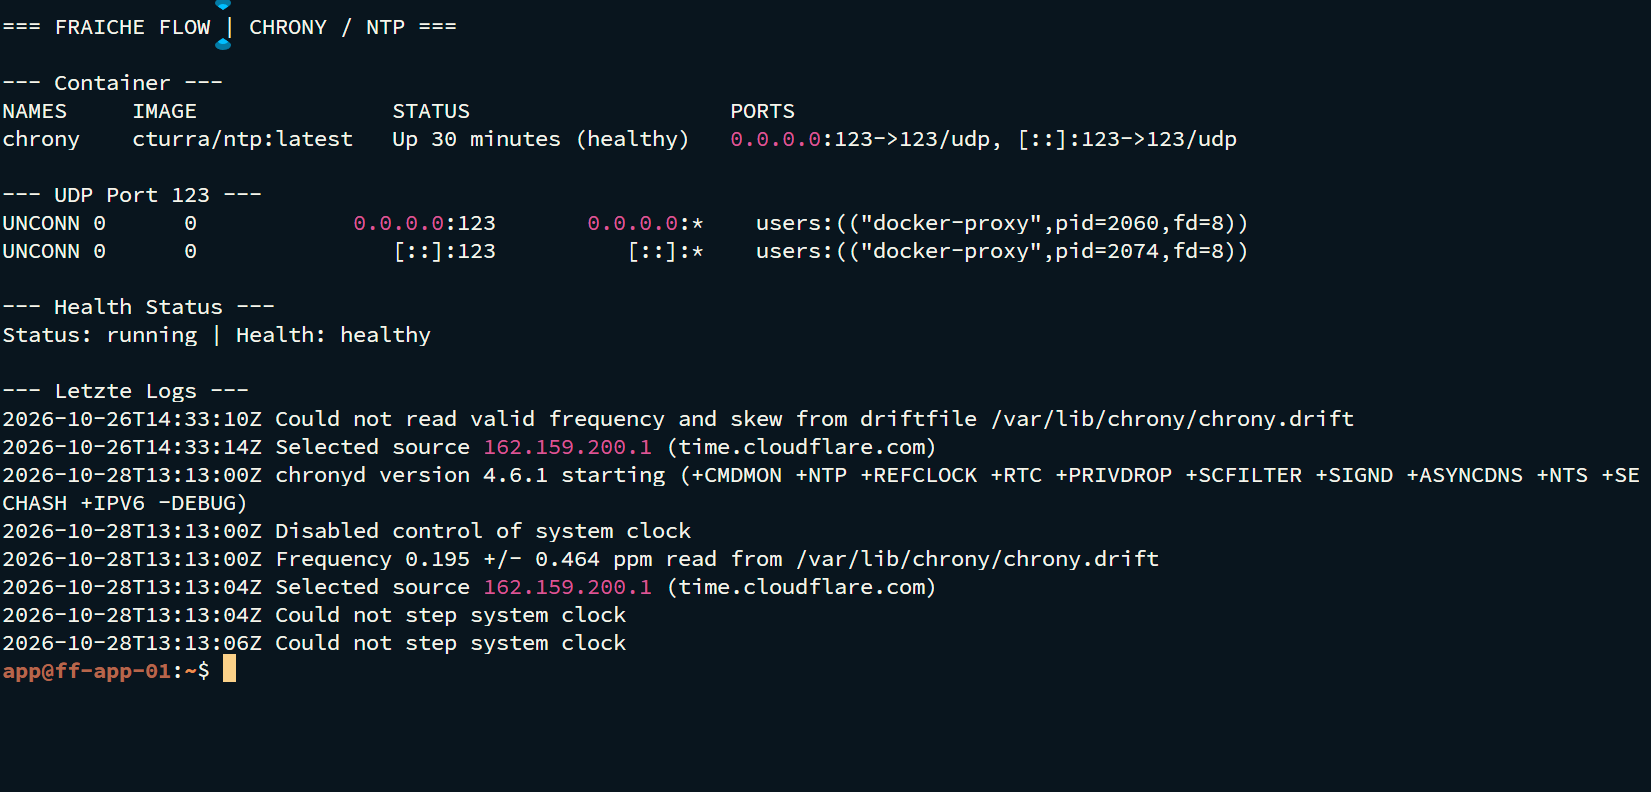
Docker showed chrony as Up (healthy) with UDP/123 published. Chrony Container is online in the final screenshot.
Verification and operational evidence
docker ps --filter name=chrony
docker logs --tail 30 chrony
sudo ss -lunp | grep ":123"
Practical troubleshooting
A ping monitor only proves reachability of the container host. It demonstrates neither a correct clock offset nor successful client NTP synchronisation.
Security and technical context
Check time sources, permitted clients and UDP reachability separately for production. Avoid unintended public NTP exposure.
Transferable skills
UDP services, container health checks and distinguishing reachability from service functionality.
Project status
Completed according to confirmation from the project lead.
17_Chrony_NTP.mdx