79 lines3.50 KB
Security analysis and measures planning
Initial situation
The security analysis is based on the saved state M02-Legacy-Baseline.
The objective of day 3 was to systematically record security-relevant conditions, assess protection needs and the resulting risks, and plan suitable security measures.
The documented legacy baseline was not hardened or otherwise modified from a security perspective.
Technical findings
| ID | Finding | Affected object | Observed condition |
|---|---|---|---|
| F01 | Extended domain administrator memberships | Active Directory | In addition to the built-in administrator, admin, martin.vogel, julia.becker and svc-backup are members of Domänen-Admins. |
| F02 | Privileged service account | svc-backup |
The enabled service account is a member of Domänen-Admins and uses a password that never expires. |
| F03 | Non-expiring service account passwords | svc-backup, svc-fsreport |
PasswordNeverExpires is enabled for both service accounts. |
| F04 | Inappropriate group nesting | AD groups | Role and permission groups have some unrelated or mutual memberships. |
| F05 | Obsolete group membership | markus.weber |
The disabled user account is still a member of a business role group. |
| F06 | Direct GPO delegation | sophie.lang |
The user account has GpoEditDeleteModifySecurity on GPO-BENUTZER-BASIS. |
| F07 | Direct NTFS permissions | FS01 |
p.mueller has Modify on Vertrieb. felix.wagner has ReadAndExecute on Technik. |
| F08 | Shared initial passwords | User and service accounts | Several accounts were created with shared initial passwords. A password change at first sign-in was not enforced. |
Technical evidence
Privileged accounts
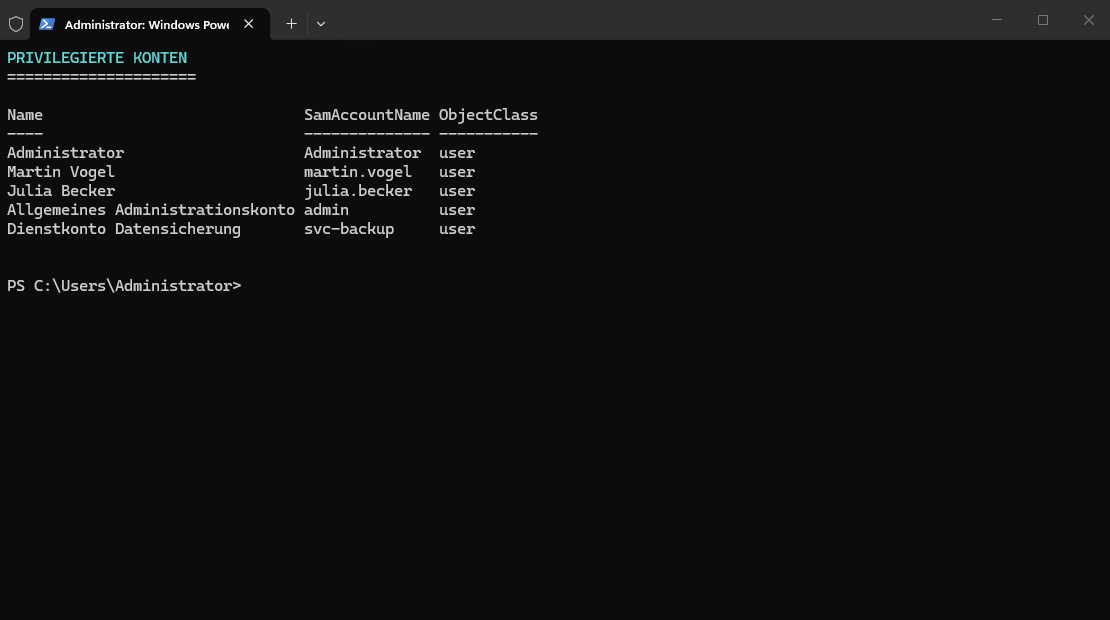
The Domänen-Admins group contains several personal accounts and the service account svc-backup.
GPO delegation
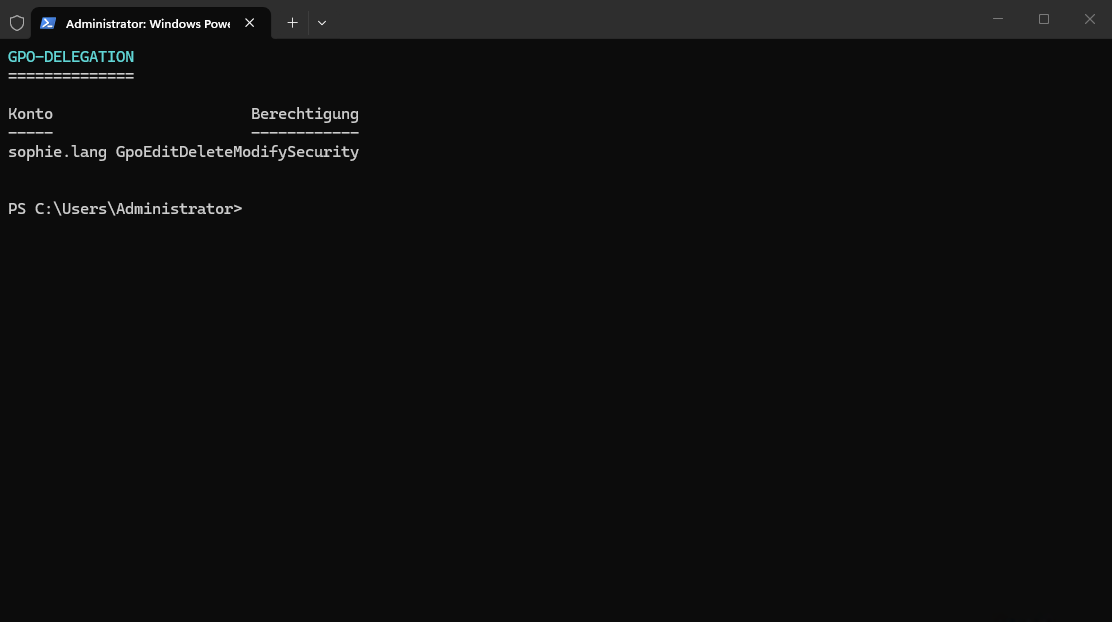
The user account sophie.lang has direct administrative permissions on GPO-BENUTZER-BASIS.
Direct NTFS permissions
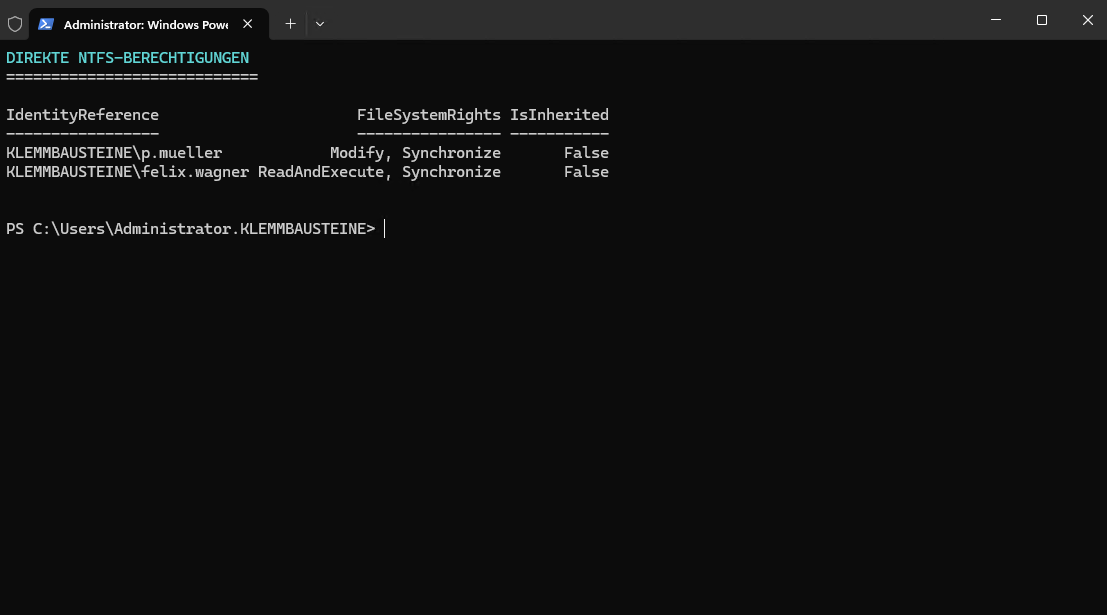
The permissions for p.mueller and felix.wagner were assigned directly to the departmental folders.
IsInherited = False confirms that the permissions were not inherited from a parent folder.
Assets requiring protection
| ID | Asset | Purpose and function | Related findings |
|---|---|---|---|
| S01 | Active Directory on DC01 |
Central management of users, groups, computers and policies | F01, F02, F04, F05, F08 |
| S02 | DNS service on DC01 |
Internal name resolution and discovery of domain services | Dependency on S01 and S05 |
| S03 | Identities and permissions | Control of sign-ins, roles, administrative rights and service accounts | F01 to F08 |
| S04 | Departmental data and SMB shares on FS01 |
Central provision of data for the business departments | F04, F05, F07 |
| S05 | RTR01 and network communication |
Routing between client, server, expansion and transit networks | Dependency of all central services |
Technical dependencies
CL01
└── DNS on DC01
    └── Active Directory

CL01
└── RTR01
    └── FS01

FS01
└── Active Directory
    └── Role and ACL groups

GPO processing
└── DC01 and SYSVOL
    ├── CL01
    └── FS01

Service accounts
└── Active Directory
    └── Services and scheduled tasks
07_sicherheitsanalyse-und-massnahmenplanung.md