Technical legacy baseline
Objective
Provision and technically verify the intended initial state for Active Directory, Group Policy, the file server, client and router.
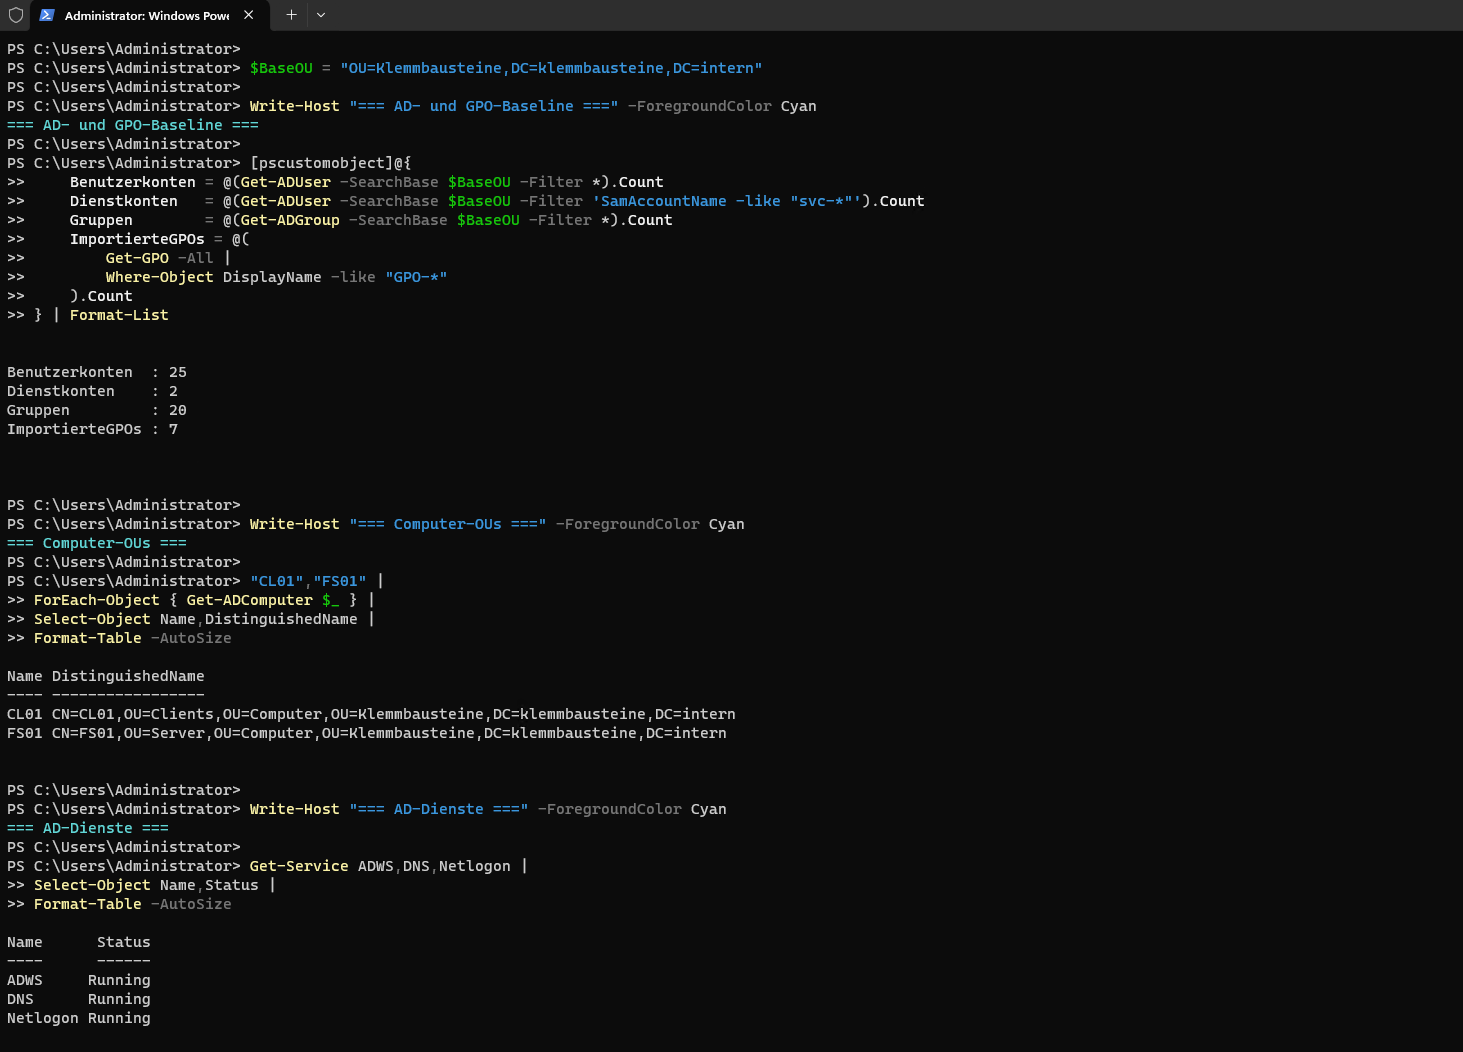
Active Directory and Group Policy
| Area | Result |
|---|---|
| Total user accounts | 25 |
| of which service accounts | 2 |
| Groups | 20 |
| Imported GPOs | 7 |
| GPO links | 8 |
| GPO delegations | 1 |
CL01 was moved to OU=Clients,OU=Computer. FS01 was moved to OU=Server,OU=Computer. The client and server policies were processed successfully.
The services ADWS, DNS and Netlogon ran without errors. The test accounts tst-technik, tst-leitung and tst-ohnezugriff, as well as the accounts admin, svc-fsreport and svc-backup, were present and enabled.
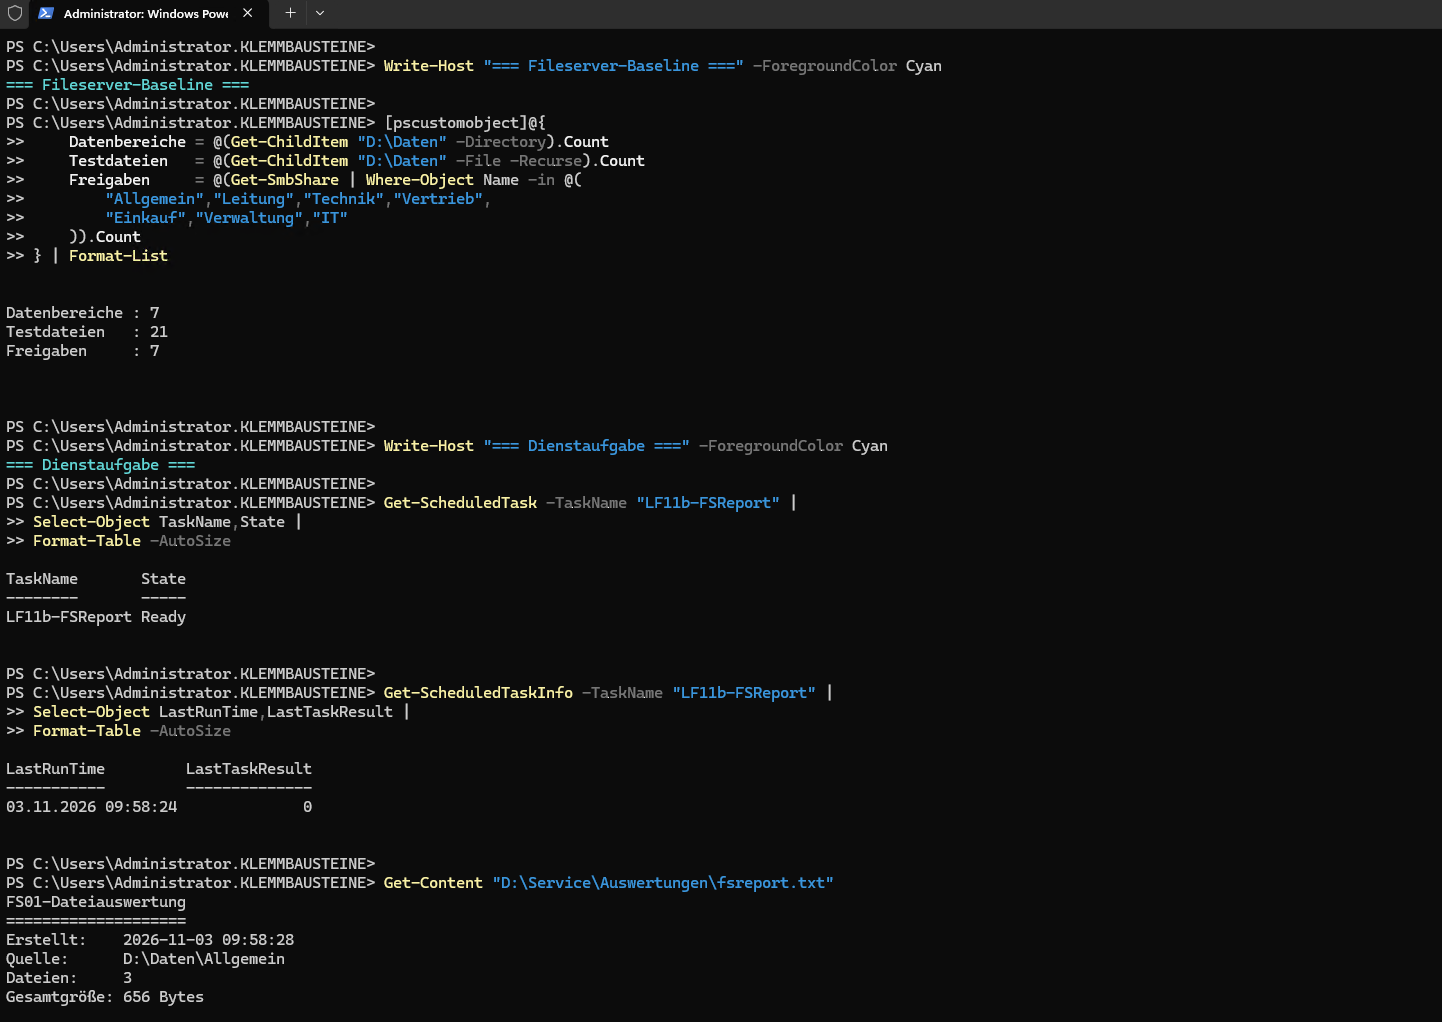
File server baseline
| Area | Result |
|---|---|
| Data volume | D: / NTFS / DATEN |
| Data areas | 7 |
| Test files | 21 |
| SMB shares | 7 |
| Direct user permissions | 2 |
The NTFS permissions were implemented using the groups ACL-FS-*-R and ACL-FS-*-RW. An authorized access attempt with tst-technik succeeded. An unauthorized access attempt with tst-ohnezugriff was denied.
Technical service task
The task LF11b-FSReport runs under KLEMMBAUSTEINE\svc-fsreport.
| Setting | Value |
|---|---|
| Source | D:\Daten\Allgemein |
| Script | D:\Service\Scripts\fsreport.ps1 |
| Output | D:\Service\Auswertungen\fsreport.txt |
| Execution right | Log on as a batch job |
| Last result | 0 |
The report contained three files from the area Allgemein and was generated successfully.
Client and router state
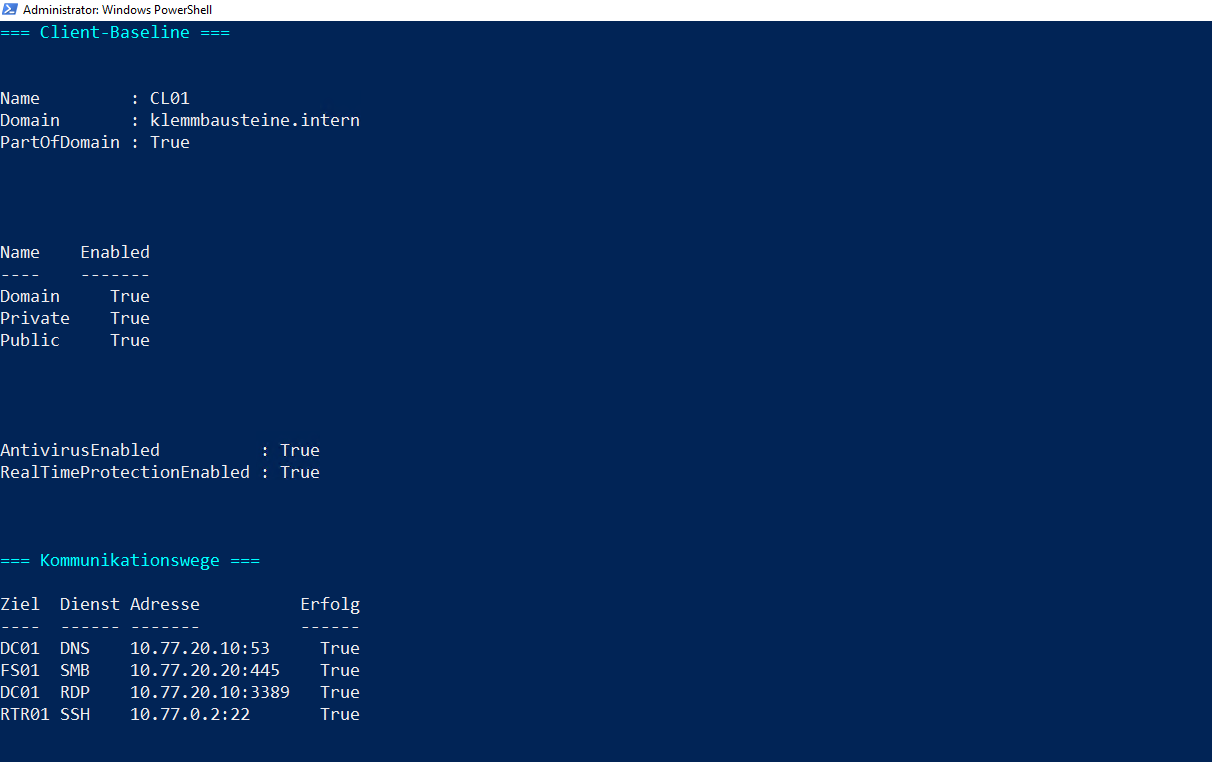
CL01 is a member of the domain klemmbausteine.intern. Windows Firewall, Microsoft Defender and real-time protection were enabled.
RTR01 provided the following networks:
| Interface | Network |
|---|---|
eth0 |
10.77.0.2/29 |
eth1.10 |
10.77.10.1/23 |
eth1.20 |
10.77.20.1/24 |
eth1.30 |
10.77.30.1/24 |
IPv4 forwarding, nftables, NAT and SSH were active.
Communication checks
| Connection | Service | Result |
|---|---|---|
CL01 → DC01 |
DNS, TCP 53 | successful |
CL01 → FS01 |
SMB, TCP 445 | successful |
CL01 → DC01 |
RDP, TCP 3389 | successful |
CL01 → RTR01 |
SSH, TCP 22 | successful |
In addition, nonexistent DNS names, an invalid SMB path, an unreachable test service, an invalid domain sign-in and an unauthorized file server access attempt were successfully rejected.
Evidence
AD and GPO baseline
File server and service task
Client, router and communication
Milestone
For the following systems, the checkpoint M02-Legacy-Baseline was created:
RTR01DC01FS01CL01
The technical legacy baseline is therefore saved reproducibly. Unexpected technical errors were corrected and then checked again.